Overview
This unit introduces you to the processes and controls for protecting organisations from cyber security threats. You will learn about management controls such as security governance and policy, risk management, and auditing, as well as processes involving employees and end users that contribute to the protection of an organisation's assets. With recent attacks as case studies, this unit will prepare you to select a range of non-technical measures to minimise future cyber security threats.
Details
Pre-requisites or Co-requisites
Pre-requisite: COIT11238 Network Infrastructure Foundations and COIT11223 Information Technology and Society
Important note: Students enrolled in a subsequent unit who failed their pre-requisite unit, should drop the subsequent unit before the census date or within 10 working days of Fail grade notification. Students who do not drop the unit in this timeframe cannot later drop the unit without academic and financial liability. See details in the Assessment Policy and Procedure (Higher Education Coursework).
Offerings For Term 3 - 2026
Attendance Requirements
All on-campus students are expected to attend scheduled classes - in some units, these classes are identified as a mandatory (pass/fail) component and attendance is compulsory. International students, on a student visa, must maintain a full time study load and meet both attendance and academic progress requirements in each study period (satisfactory attendance for International students is defined as maintaining at least an 80% attendance record).
Recommended Student Time Commitment
Each 6-credit Undergraduate unit at CQUniversity requires an overall time commitment of an average of 12.5 hours of study per week, making a total of 150 hours for the unit.
Class Timetable
Assessment Overview
| Assessment Task | Part Weighting (% of assessment) |
Assessment Security Level | Gen AI Guidance Levels |
|---|---|---|---|
| 1. Assessment 1 - Portfolio (40% of unit ) | |||
| Portfolio (Portfolio) | 100% of 40% | Low | AI-Assisted (Guided Collaboration) |
| 2. Assessment 2: Group Assessment (20% of unit ) | |||
| Presentation (Presentation) | 100% of 20% | Medium | No Gen AI Use |
| 3. Assessment 3: Report (40% of unit ) | |||
| Report (Project (applied)) | 100% of 40% | Medium | AI-Assisted (Guided Collaboration) |
Assessment Grading
This is a graded unit: your overall grade will be calculated from the marks or grades for each assessment task, based on the relative weightings shown in the table above. You must obtain an overall mark for the unit of at least 50%, or an overall grade of 'pass' in order to pass the unit. If any 'pass/fail' tasks are shown in the table above they must also be completed successfully ('pass' grade). You must also meet any minimum mark requirements specified for a particular assessment task, as detailed in the 'assessment task' section (note that in some instances, the minimum mark for a task may be greater than 50%). Consult the University's Grades and Results Policy for more details of interim results and final grades.
All University policies are available on the CQUniversity Policy site.
You may wish to view these policies:
- Grades and Results Policy
- Assessment Policy and Procedure (Higher Education Coursework)
- Review of Grade Procedure
- Student Academic Integrity Policy and Procedure
- Academic Progression Policy and Procedure
- Student Refund and Credit Balance Policy and Procedure
- Complaints Policy and Procedure
- Information and Communications Technology Acceptable Use Policy and Procedure
This list is not an exhaustive list of all University policies. The full list of University policies are available on the CQUniversity Policy site.
Feedback, Recommendations and Responses
Every unit is reviewed for enhancement each year. At the most recent review, the following staff and student feedback items were identified and recommendations were made.
Feedback from In-Class student verbal feedback, T2,2025
Student-to-student engagement was limited.
In the Week 3 workshop, incorporate a group-based peer learning activity in which students analyse a cybersecurity risk scenario, present their findings, and receive structured peer feedback. This approach should support collaborative learning by exposing students to alternative perspectives.
- Discuss the best practice principles, processes and standards in cyber security
- Compare the role of management, operational and technical controls in delivering cyber security
- Conduct an organisational cyber security risk analysis
- Prepare plans for auditing security controls and recovering from security attacks
- Explain techniques for managing people to ensure secure IT systems.
The Australian Computer Society (ACS), the professional association for Australia's ICT sector, recognises the Skills Framework for the Information Age (SFIA). SFIA is adopted by organisations, governments, and individuals in many countries, providing a widely used and consistent definition of ICT skills. SFIA is increasingly being used when developing job descriptions and role profiles. ACS members can use the tool MySFIA to build a skills profile.
This unit contributes to the following workplace skills as defined by SFIA 9 (the SFIA code is included):
- Audit (AUDT)
- Risk management (BURM)
- Continuity management (COPL)
- Information Assurance (INAS)
- Information Security (SCTY)
Alignment of Assessment Tasks to Learning Outcomes
| Assessment Tasks | Learning Outcomes | ||||
|---|---|---|---|---|---|
| 1 | 2 | 3 | 4 | 5 | |
|
1.
Assessment 1
(40% of unit )
Portfolio
|
|||||
|
2.
Assessment 2
(20% of unit )
Presentation
|
|||||
|
3.
Assessment 3
(40% of unit )
Project (applied)
|
|||||
Alignment of Graduate Attributes to Learning Outcomes
| Graduate Attributes | Learning Outcomes | ||||
|---|---|---|---|---|---|
| 1 | 2 | 3 | 4 | 5 | |
| 1 - Communication | |||||
| 2 - Problem Solving | |||||
| 3 - Critical Thinking | |||||
| 4 - Information Literacy | |||||
| 5 - Team Work | |||||
| 6 - Information Technology Competence | |||||
| 7 - Cross Cultural Competence | |||||
| 8 - Ethical practice | |||||
| 9 - Social Innovation | |||||
| 10 - First Nations Knowledges | |||||
Textbooks
There are no required textbooks.
IT Resources
- CQUniversity Student Email
- Internet
- Unit Website (Moodle)
All submissions for this unit must use the referencing style: Harvard (author-date)
For further information, see the Assessment Tasks.
a.shahidinejad@cqu.edu.au
Week 1
Begin Date: 09 Nov 2026Module/Topic
Introduction to Cybersecurity Management
Chapter
Online resources supplied
Events and Submissions/Topic
Class introduction
Week 2
Begin Date: 16 Nov 2026Module/Topic
Cybersecurity Roles and Responsibilities
Chapter
Online resources supplied
Events and Submissions/Topic
Week 3
Begin Date: 23 Nov 2026Module/Topic
Management of Cybersecurity Risk
Chapter
Online resources supplied
Events and Submissions/Topic
Weekly Portfolio
Week 4
Begin Date: 30 Nov 2026Module/Topic
NIST Cybersecurity Framework
Chapter
Online resources supplied
Events and Submissions/Topic
Weekly Portfolio
Week 5
Begin Date: 07 Dec 2026Module/Topic
Cybersecurity Policy
Chapter
Online resources supplied
Events and Submissions/Topic
Week 6
Begin Date: 14 Dec 2026Module/Topic
Cybersecurity Risk Mitigation and
Treatment
Chapter
Online resources supplied
Events and Submissions/Topic
Mid-Term Break
Begin Date: 21 Dec 2026Module/Topic
Chapter
Events and Submissions/Topic
Week 7
Begin Date: 04 Jan 2027Module/Topic
In-class Presentation
Chapter
Online resources supplied
Events and Submissions/Topic
Week 8
Begin Date: 11 Jan 2027Module/Topic
Cybersecurity Contingency Planning
Chapter
Online resources supplied
Events and Submissions/Topic
Week 9
Begin Date: 18 Jan 2027Module/Topic
Managing Cybersecurity in Cloud
Computing
Chapter
Online resources supplied
Events and Submissions/Topic
Week 10
Begin Date: 25 Jan 2027Module/Topic
Cybersecurity Technical Measures
Chapter
Online resources supplied
Events and Submissions/Topic
Weekly Portfolio
Week 11
Begin Date: 01 Feb 2027Module/Topic
SME Cybersecurity Guidelines
Chapter
Online resources supplied
Events and Submissions/Topic
Week 12
Begin Date: 08 Feb 2027Module/Topic
Ethical Challenges for
Cybersecurity
Chapter
Online resources supplied
Events and Submissions/Topic
Exam Week
Begin Date: 15 Feb 2027Module/Topic
Chapter
Events and Submissions/Topic
Ali Shahidinejad
Unit Coordinator, Lecturer, Tutor
Email address: a.shahidinejad@cqu.edu.au
1. Assessment 1 - Portfolio ( 40% of unit )
Portfolio
This is an individual assessment. During your weekly workshops, you will conduct Cybersecurity management activities for given case studies, such as developing policies and preparing plans. You must maintain your responses from the workshop activities in an online portfolio. This assessment is due in week 9.
Week 9 Friday (22 Jan 2027) 11:45 pm AEST
Week 10 Friday (29 Jan 2027)
- Completion of Weekly Workshop Activities (30 marks): Complete the required workshop activities for Weeks 1–9, providing evidence of participation and task completion.
- Application of Cybersecurity Management Concepts (20 marks): Demonstrate understanding and appropriate application of cybersecurity management concepts to case studies, with justified and professional solutions.
- Quality of Analysis and Problem-Solving (25 marks): Provide critical analysis, identify relevant issues, and develop logical, well-supported recommendations.
- Organisation and Presentation (15 marks): Present a well-organised portfolio with clear weekly sections, consistent formatting, and a professional structure.
- Communication and Academic Integrity (10 marks): Communicate clearly and professionally, use appropriate referencing, and acknowledge generative AI use where applicable.
- Discuss the best practice principles, processes and standards in cyber security
- Compare the role of management, operational and technical controls in delivering cyber security
- Conduct an organisational cyber security risk analysis
- Prepare plans for auditing security controls and recovering from security attacks
- Explain techniques for managing people to ensure secure IT systems.
2. Assessment 2: Group Assessment ( 20% of unit )
Presentation
This assessment can be undertaken in a group with 3 to 4 students.
In this assessment, you are to prepare an Issue Specific Security Policy (ISSP) for a given case study. Your group will be allocated 10 minutes in class to present the ISSP. Distance students will have the option to submit a recording of the presentation in lieu of doing it live in class. Other students may discuss taking this option with the unit coordinator. Details of the marking criteria will be available on the Moodle unit website.
Week 7 Friday (8 Jan 2027) 11:45 pm AEST
Week 8 Friday (15 Jan 2027)
Understanding of the case study and identification of key cybersecurity issues: 4
Quality, relevance, and completeness of the proposed ISSP: 5
Justification using cybersecurity frameworks, standards, and regulations: 4
Practicality of implementation, governance, monitoring, and enforcement strategies: 3
Presentation quality, structure, clarity, timing, and group contribution: 2
References, and academic integrity: 2
- Discuss the best practice principles, processes and standards in cyber security
- Compare the role of management, operational and technical controls in delivering cyber security
- Conduct an organisational cyber security risk analysis
3. Assessment 3: Report ( 40% of unit )
Project (applied)
You will conduct a comprehensive cybersecurity risk management analysis for a given case study. You may use either a recognised risk management framework or the NIST Cybersecurity Framework. The output will be a written report.
This assessment can be undertaken in a group with 3 to 4 students.
Week 12 Friday (12 Feb 2027) 11:45 pm AEST
Exam Week Friday (19 Feb 2027)
- Risk Analysis Quality (12 marks): Identify and evaluate relevant risks using credible threat, vulnerability and consequence relationships, appropriate risk ratings, supporting evidence and required frameworks, including gaps in AI-generated analysis.
- Risk Treatment and Control Architecture (12 marks): Recommend practical, integrated security controls aligned with the Essential Eight and NIST CSF, addressing relevant technology, privacy, supplier and payment risks, and justifying residual risk.
- Incident Response (12 marks): Develop a scenario-specific incident response plan covering all phases, priorities, evidence preservation, business continuity, stakeholder communication and regulatory considerations.
- AI Critique and Professional Judgement (8 marks): Document AI interactions, critically verify outputs, justify decisions to accept, modify or reject recommendations, and demonstrate human responsibility for final decisions.
- Critical Reflection (4 marks): Provide an honest and analytical reflection addressing all required questions and supported by specific examples.
- Professional Presentation (2 marks): Present a clearly organised and professionally written submission with effective tables, accurate referencing, compliance with submission requirements and a complete group contribution statement.
- Prepare plans for auditing security controls and recovering from security attacks
- Explain techniques for managing people to ensure secure IT systems.
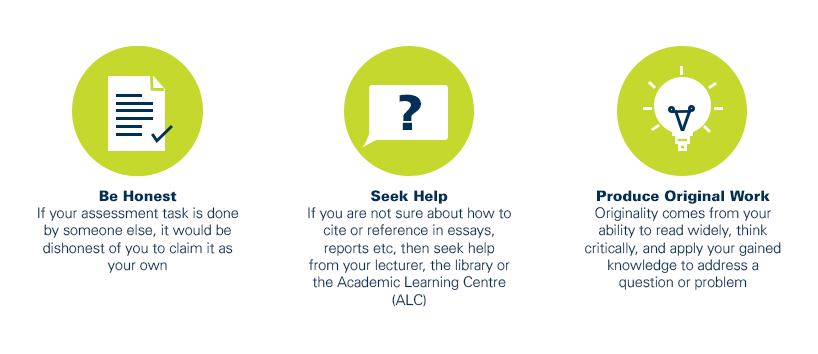
As a CQUniversity student you are expected to act honestly in all aspects of your academic work.
Any assessable work undertaken or submitted for review or assessment must be your own work. Assessable work is any type of work you do to meet the assessment requirements in the unit, including draft work submitted for review and feedback and final work to be assessed.
When you use the ideas, words or data of others in your assessment, you must thoroughly and clearly acknowledge the source of this information by using the correct referencing style for your unit. Using others’ work without proper acknowledgement may be considered a form of intellectual dishonesty.
Participating honestly, respectfully, responsibly, and fairly in your university study ensures the CQUniversity qualification you earn will be valued as a true indication of your individual academic achievement and will continue to receive the respect and recognition it deserves.
As a student, you are responsible for reading and following CQUniversity’s policies, including the Student Academic Integrity Policy and Procedure. This policy sets out CQUniversity’s expectations of you to act with integrity, examples of academic integrity breaches to avoid, the processes used to address alleged breaches of academic integrity, and potential penalties.
What is a breach of academic integrity?
A breach of academic integrity includes but is not limited to plagiarism, self-plagiarism, collusion, cheating, contract cheating, and academic misconduct. The Student Academic Integrity Policy and Procedure defines what these terms mean and gives examples.
Why is academic integrity important?
A breach of academic integrity may result in one or more penalties, including suspension or even expulsion from the University. It can also have negative implications for student visas and future enrolment at CQUniversity or elsewhere. Students who engage in contract cheating also risk being blackmailed by contract cheating services.
Where can I get assistance?
For academic advice and guidance, the Academic Learning Centre (ALC) can support you in becoming confident in completing assessments with integrity and of high standard.
What can you do to act with integrity?